
Bank Rakyat has disabled access to most of its websites after several of its banking pages, including the iRakyat online banking login page, were defaced in a suspected cyberattack late on Friday.
Shortly before midnight, the bank posted a notice on its social media channels after the defaced sites were taken offline. The bank did not immediately confirm the incident as a cyberattack.
The defacement was claimed by a threat actor going by the name MARLANWG. The same actor previously claimed to be offering webshell access to production MySQL databases belonging to the Royal Malaysian Customs Department.
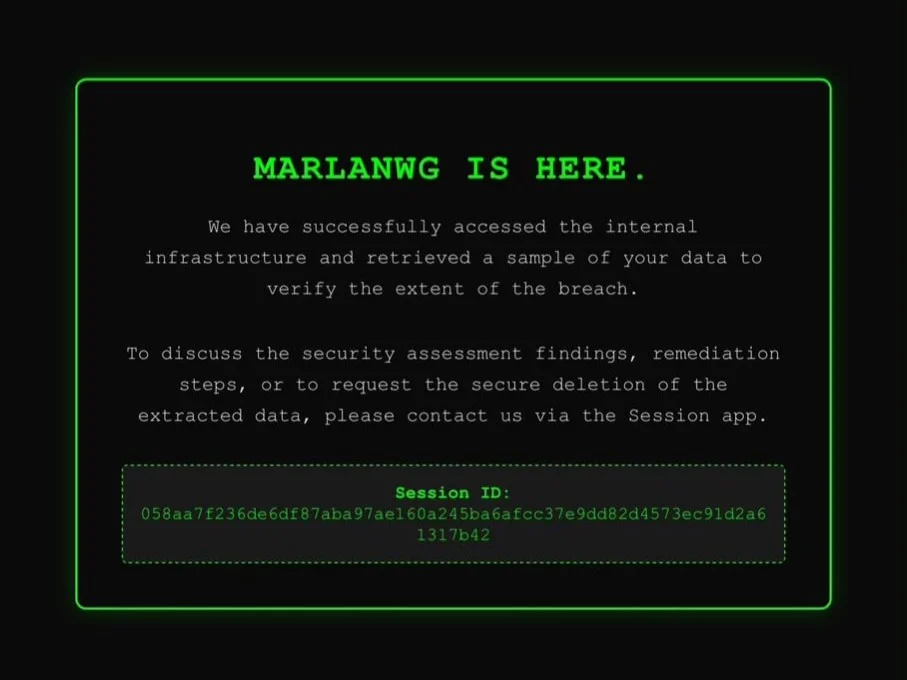
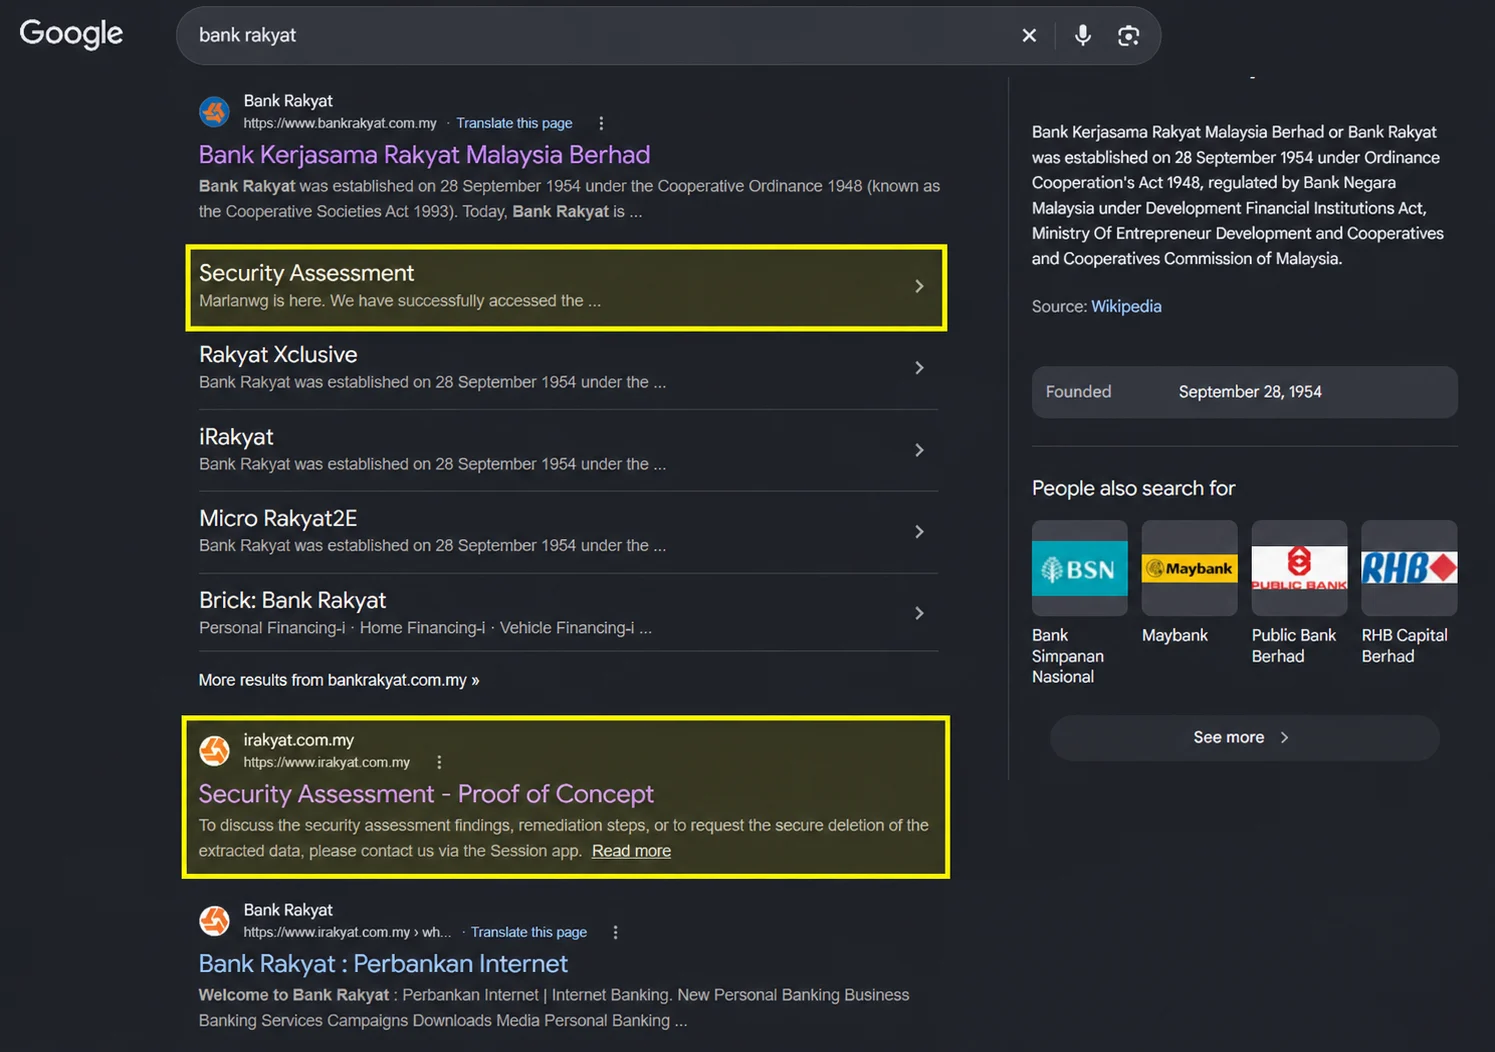
Bank Rakyat has yet to publicly acknowledge the intrusion and disclose whether any customer data was compromised in this attack. What is concerning is that the online banking pages also seem to have been compromised, across multiple domain names belonging to the bank. While the sites have since been taken down and restored – Google’s search is still showing results from the compromised pages.
What Bank Rakyat customers should do
- Avoid logging in through search engine results until they are refreshed. Type the bank’s web address directly or use the official mobile app.
- Be wary of SMS, calls or emails that refer to this incident. Scammers often use news of a breach to make phishing attempts look credible.
- Check recent account transactions and report anything unusual to the bank immediately.
This story will be updated with an official statement from Bank Rakyat once it becomes available.